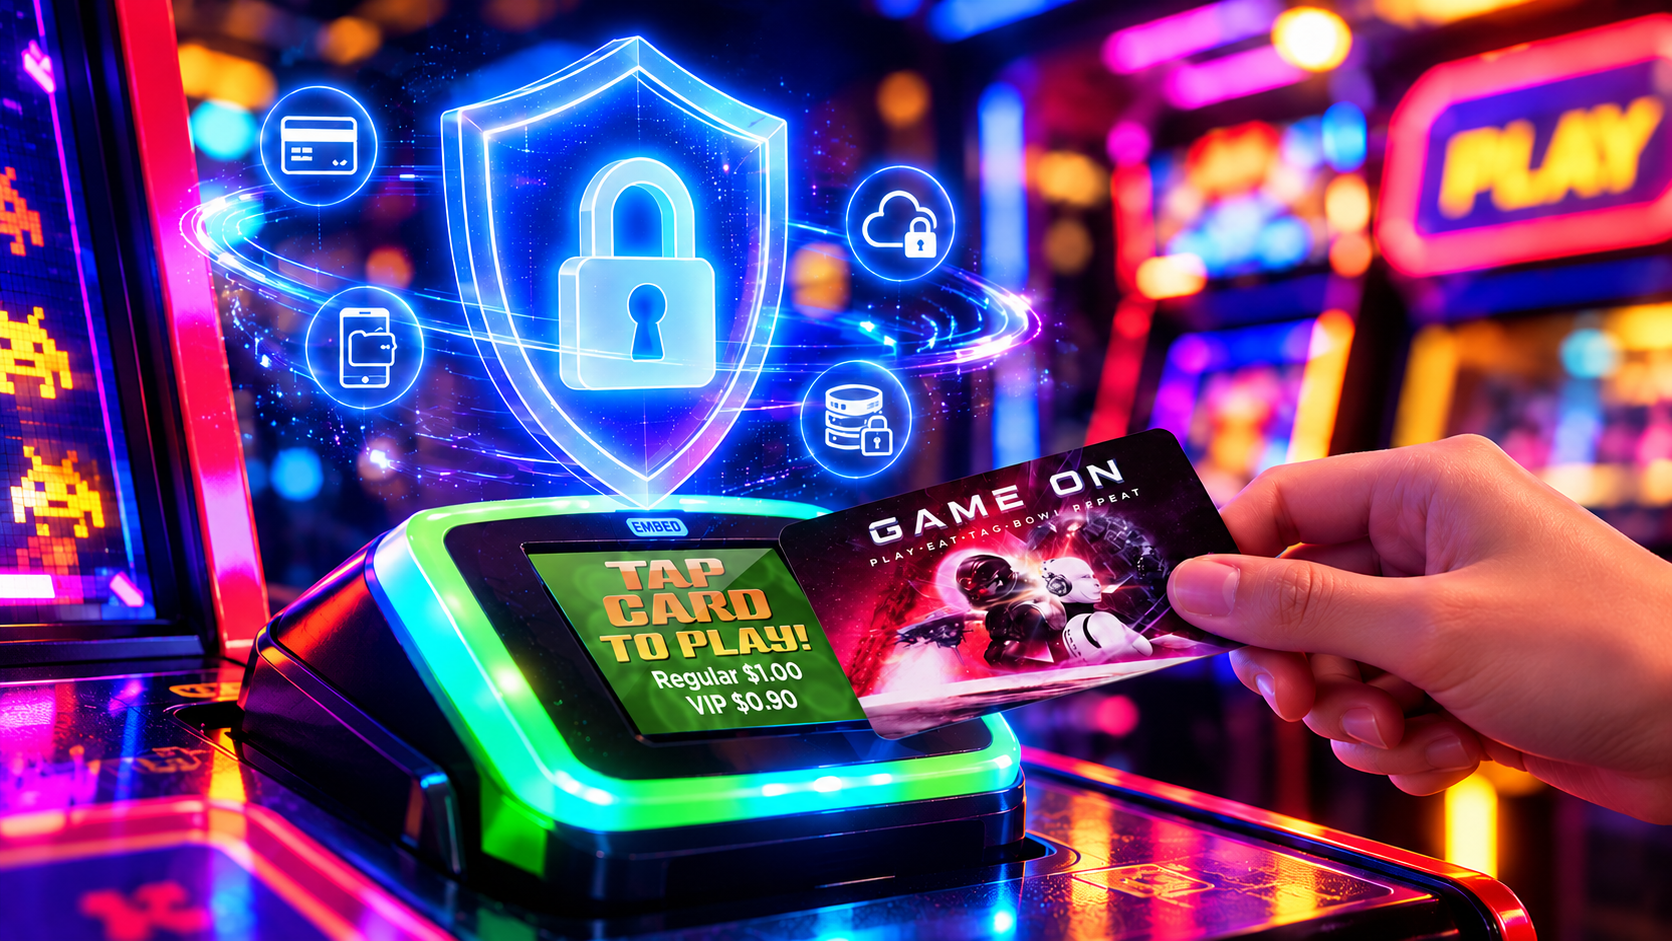
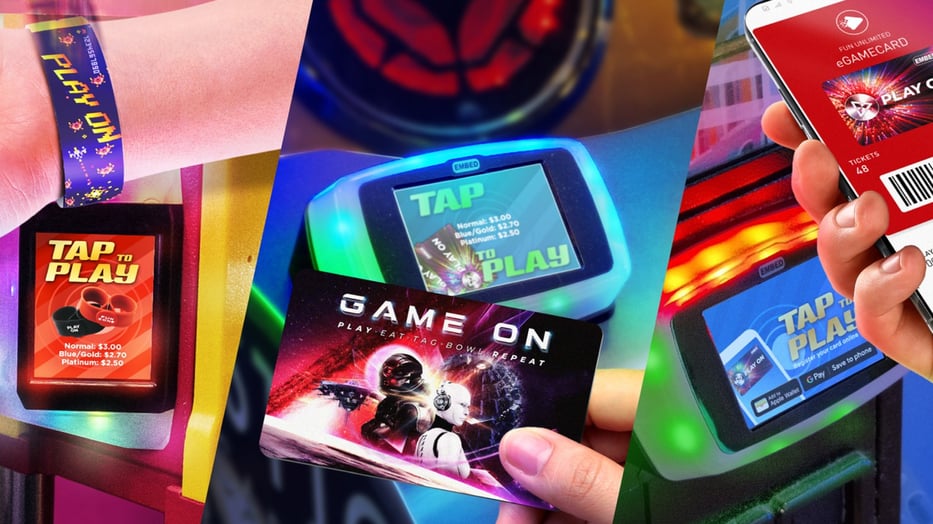
Cashless payments have transformed how family entertainment centers operate. Today’s guests expect to tap, pay, reload, and play without friction, whether they are purchasing game credits, topping up a game card, or using a Mobile Wallet.
For operators, however, convenience comes with responsibility. As more transactions move online and into cashless ecosystems, protecting payment data is critical. A cashless arcade system itself should not automatically be described as “PCI-compliant.” Rather, operators should understand which payment systems, processors, service providers, and components interact with cardholder data and ensure they meet the appropriate PCI DSS requirements.
PCI DSS establishes technical and operational requirements designed to protect cardholder data. Maintaining payment security applies to entities that store, process, or transmit credit card data.
Why does PCI compliance matter for your FEC?
Every card tap, Mobile Wallet reload, kiosk transaction, and online purchase creates an opportunity to improve guest convenience. It also introduces potential risk if payment systems are not properly secured.
PCI DSS (Payment Card Industry Data Security Standard) establishes requirements designed to protect cardholder data and payment environments. PCI SSC provides different self-assessment questionnaires for different merchant environments, meaning the requirements relevant to an FEC depend partly on how its payments are accepted and processed.
For family entertainment centers, working with PCI-compliant payment processors and service providers, while maintaining the venue’s own applicable PCI DSS requirements, can help operators:
-
- Protect guest payment information
- Reduce exposure to cardholder data
- Reduce the risk of payment-data breaches
- Maintain guest trust
- Support secure cashless payment experiences
- Manage financial and reputational risk
- Meet applicable payment-security requirements
As venues continue to adopt cashless technology, understanding the payment environment surrounding the cashless ecosystem becomes a foundational part of modern FEC operations.
What are the business risks of non-compliant payment systems?
Many operators view PCI compliance as purely a technical requirement. In reality, payment security can have significant operational and commercial consequences.
A payment security incident may lead to business disruption, remediation costs, restrictions imposed by payment partners, reputational damage, and loss of guest confidence.
Beyond the immediate impact of an incident, families expect venues to handle their payment information responsibly. For modern FECs, payment security has therefore become an important part of protecting the overall guest experience.
How can secure payment systems protect your guests’ payment data?
Modern payment technologies can provide layers of protection that help secure cardholder data while supporting a seamless guest experience.
1. Point-to-Point Encryption (P2PE)
Payment solutions may use encryption technologies to protect payment data as it moves through the payment process. When evaluating a processor or payment provider, operators should understand what encryption technologies are used and which components of the transaction they protect.
2. Tokenisation
Payment providers may use tokenisation to replace sensitive payment card information with a substitute value or token. Depending on the payment solution, tokenization can support experiences such as:
- Mobile Wallet reloads
- Saved payment methods
- Repeat purchases
- Account top-ups
Operators should verify with their processor or payment provider how cardholder data is handled, tokenized, transmitted, and stored, and what responsibilities remain within the merchant's own PCI scope.
3. Integrated Payment Security
Payment Integration can help FECs create a more seamless guest experience, but integration by itself does not make a cashless system PCI-compliant.
Operators should understand where the payment transaction takes place, which systems or providers encounter cardholder data, and where responsibility for securing that data sits.
That's particularly important because PCI SSC notes that even service providers that don't store, process, or transmit cardholder data can potentially affect the security of a cardholder's data environment through their access.
How should you choose payment solutions for your
cashless arcade system?
Not all payment solutions offer the same security capabilities. When evaluating payment processing options for your FEC, look beyond basic card acceptance and understand both the provider's PCI DSS status and your own responsibilities as the merchant.
1. Verify your payment provider's PCI DSS status.
Ask payment processors and relevant service providers about their current PCI DSS compliance status and which parts of the payment environment their compliance covers. Choosing a PCI-compliant processor does not automatically make your FEC PCI-compliant.
PCI SSC specifically encourages customers to use service providers that can demonstrate PCI DSS compliance covering the services being provided, while also advising customers to understand how those providers interact with their cardholder data environment.
2. Understand your merchant responsibilities.
Ask your processor or PCI compliance provider for which requirements apply to your specific payment environment and what validation is required.
PCI SSC notes that organisations should work with the organisations managing their compliance programs, such as their acquirer or payment brands, to determine specific PCI DSS validation and reporting requirements.
3. Support modern payment preferences.
Guests increasingly expect convenient digital payment experiences, including contactless payments and digital wallets. Operators should ensure the payment providers supporting these experiences meet the appropriate security requirements.
4. Understand the full payment ecosystem.
Your cashless platform may integrate game cards, kiosks, Mobile Wallets, loyalty functionality, reporting, and payment processing. Not every component is necessarily part of the PCI DSS environment. The important question is how each component interacts with the systems responsible for accepting and processing payment card data.
Questions to ask your payment processor about PCI compliance
- What is your current PCI DSS compliance status, and which payment services does that compliance cover?
- Which parts of my FEC's payment environment remain my responsibility as the merchant?
- Which self-assessment questionnaire (SAQ) or other validation requirements apply to my business?
- Do you provide or recommend a PCI compliance provider to help merchants complete their validation requirements?
- How is cardholder data protected when a transaction is processed?
- Does your payment solution use encryption and/or tokenization, and where are those technologies applied?
- Does any cardholder data enter or remain within my venue's systems or network?
- Are vulnerability scans required for my payment environment, and if so, do I need an Approved Scanning Vendor (ASV)?
- What ongoing PCI DSS responsibilities will my business have after the payment system is installed?
- If my payment environment changes, how could that affect my PCI DSS scope or validation requirements?
Building secure cashless experiences
A cashless infrastructure can combine secure payment processing with technologies designed to improve venue efficiency, and overall guest experience.
Within the Embed Ecosystem:
-
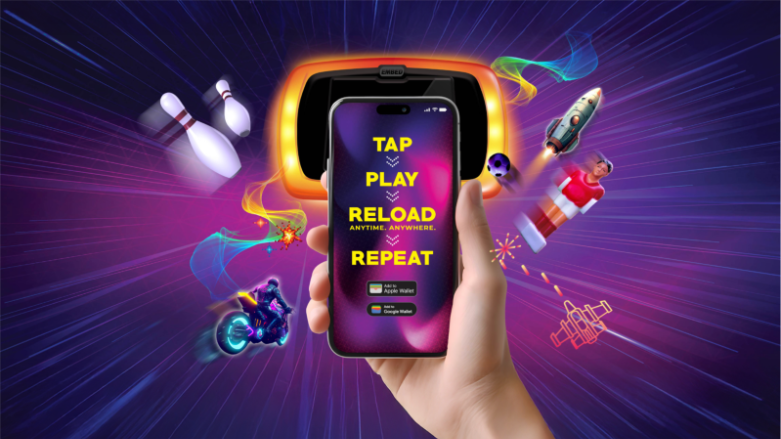
smartTOUCH+ arcade game card readers can support cashless gameplay while providing operators with greater visibility into guest behavior and venue performance. Game card and Mobile Wallet-compatible; guests can tap and play without cumbersome tickets and coins.
- Mobile Wallet is a virtual game card that sits on guests’ Apple Pay or Google Pay, enabling them to pay and play with their smartphones. This Apple and Google-certified solution is powered with mobile encryption technology for advanced security.
Protecting payments within the cashless FEC
PCI compliance is an important part of operating a secure, modern family entertainment center, but it is important to understand where that compliance responsibility sits.
A cashless arcade ecosystem should not automatically be characterized as “PCI compliant” simply because it integrates with card payments. Instead, FEC operators should work with payment processors and service providers that meet the appropriate PCI DSS requirements, understand how those providers protect cardholder data, and fulfil the PCI DSS responsibilities that apply to the FEC itself.
Using qualified third-party providers can help protect the payment environment, but it does not eliminate the merchant's responsibility to understand and maintain its own applicable PCI DSS requirements. PCI SSC specifically advises merchants to consider people, processes, and technology when protecting payment data.
As guest expectations continue moving towards mobile-first and cashless experiences, choosing secure payment infrastructure, understanding your payment-data environment, and maintaining your merchant PCI obligations are important steps toward protecting your venue and your guests.
Learn more about Embed's cashless ecosystem integrated with secure payment solutions here.